
Account impersonation
Mailbox Storage Alert — Quota Nearly Reached | Review of a suspicious mailbox quota warning
This message claims the mailbox is 99.9% full and warns of delivery problems. It includes the recipient's address, while its storage-management button uses a shortened URL.
Public EML case analysis · An archived 2025 message
A warning that incoming mail may stop can feel urgent. This public sample, dated 2025-09-29 in its headers, claims 99.9% storage use and asks the recipient to manage capacity. We have not verified that figure against the actual account.
An excerpt from the message
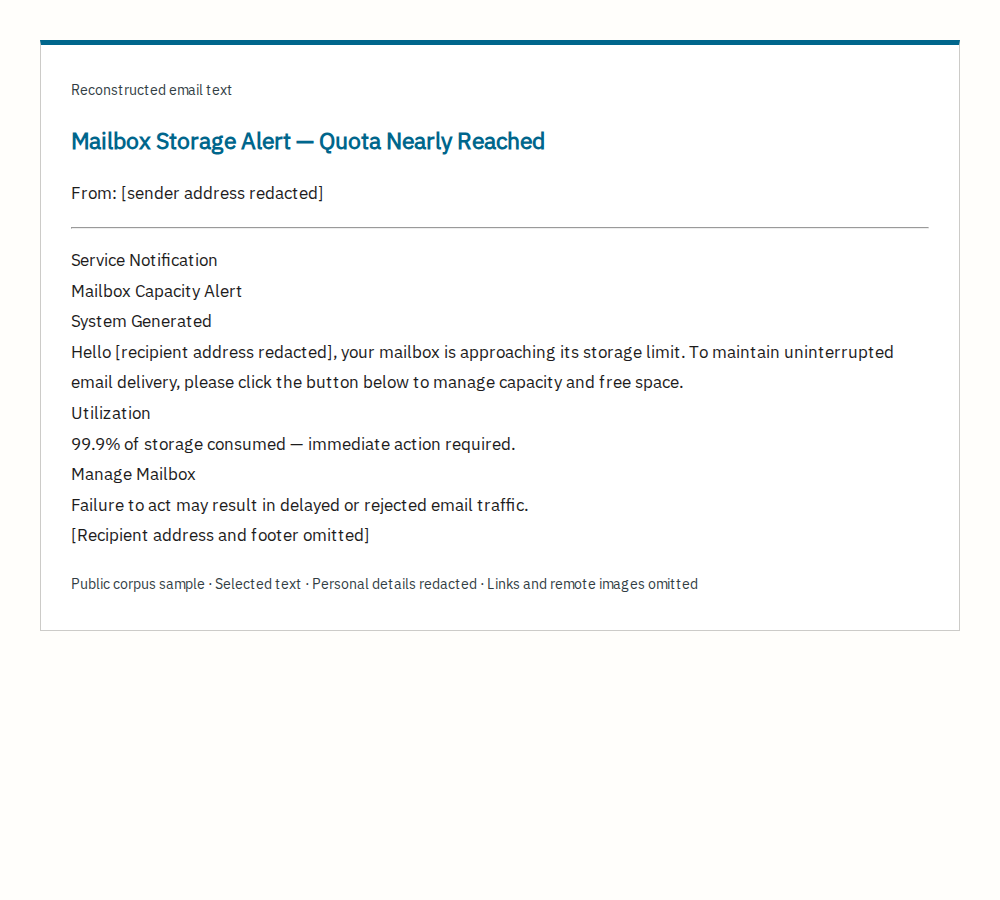
Selected text from the public EML, reconstructed for this article. Personal details are redacted; working links and remote images are omitted. This is not a screenshot of the original inbox. The original English is retained.
A personal address does not validate the warning
The body includes the recipient's email address and domain, making it resemble an individual service notification. Knowing an address does not establish that the sender has checked its storage. Those details are redacted in the public reconstruction.
The From address uses naqglobal[.]com. The Manage Mailbox button uses the shortener rb[.]gy, which conceals the final destination in the message. Shortened links are not inherently malicious, but this urgent account request leaves its verification route unclear.
The storage figure remains unverified
Our evidence is a message from a public corpus. We have no account-access record or recipient testimony confirming the storage level. The suspected-phishing assessment considers the apparent service notification, sender information and shortened link with that limitation in mind.
The headers record spf=pass, dkim=pass and dmarc=pass. These records do not validate the claimed storage level or the sender's authority to manage it. We neither expanded nor visited the link.
Check storage in the mail service itself
Open your usual mail app or webmail settings to check storage. For a company account, use an established IT contact. There is no need to submit account information through an unfamiliar link just to verify a quota warning.
Source and scope
This case uses a message extracted as EML from the 2025 Jose Nazario phishing corpus. It is a public collection sample, not an email submitted by a reader to this site. Dates refer to the message's Date header, not an independently established incident date.
We inspected saved headers, body text and embedded addresses without visiting destination sites. The selected message has no document attachments. The reconstruction removes personal details and excerpts the body; the Korean and English explanations are our own. The corpus is provided under CC BY 4.0.